GDPR compliant email marketing list management means every address on your list has a lawful basis for marketing, usually freely given, specific, informed and unambiguous consent. You must be able to prove that basis, keep the data accurate and no longer than necessary, honour data subject rights quickly, and only use vendors bound by a data processing agreement. This guide covers each of those duties and ends with an audit checklist you can run this quarter.
Understanding GDPR’s Core Requirements for Email Marketing Lists
An email address that identifies a person, including a work address like name@company.com, is personal data. Several GDPR principles apply directly to a marketing list:
- Lawfulness, fairness and transparency (Art. 5(1)(a)): people must know who is emailing them and why.
- Purpose limitation: an address collected for order receipts is not automatically fair game for newsletters.
- Data minimisation: collect an email address and perhaps a first name, not a long profile “just in case”.
- Accuracy and storage limitation: stale and unused records are a liability.
- Accountability (Art. 5(2)): you carry the burden of proving compliance.
Most advice stops at “get consent”. In practice, regulators and auditors ask for evidence, and that is where marketing teams struggle. We use a simple model, the Five Proofs: proof of consent, proof of purpose, proof of processor control, proof of hygiene, and proof of rights handling. The rest of this article follows it.
Consent as the Foundation: Explicit Opt-In, Affirmative Action & Documentation
What qualifies as GDPR-compliant consent, and how does it differ from opt-in/opt-out?
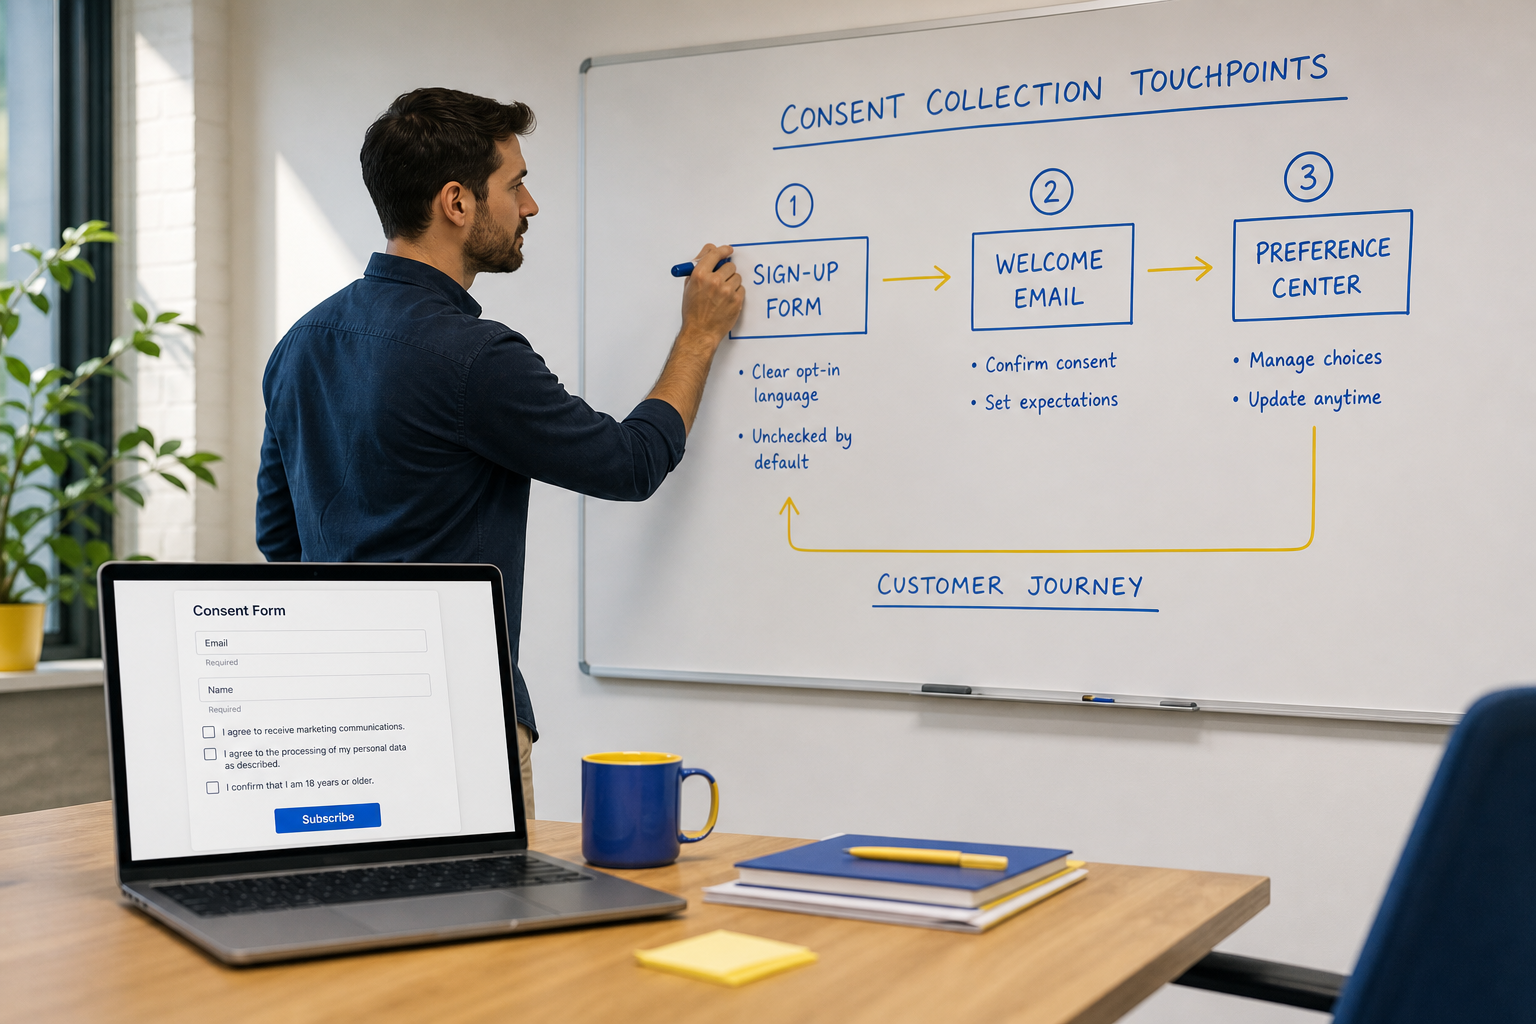
Under Article 4(11), consent must be freely given, specific, informed and unambiguous, and given by a clear affirmative act. Pre-ticked boxes, silence and inactivity do not count. This is why “opt-out” models, where people are subscribed unless they object, generally fail for consent-based marketing. “Opt-in” is only compliant if the action is genuinely affirmative and the person knows what they are agreeing to.
Consent also has to meet Article 7 conditions:
- It is separable from other terms. Do not bundle newsletter consent into a purchase or terms-of-service checkbox.
- It is as easy to withdraw as to give.
- You can demonstrate it was given.
- It is not a condition of a service that does not need the data.
Is double opt-in required?
GDPR does not mandate double opt-in, but it is the strongest way to document consent. A confirmation email proves the address belongs to the subscriber, reduces typos and fake sign-ups, and produces a timestamped record. Some national authorities, notably in Germany, effectively expect it. For list-management purposes, double opt-in GDPR workflows are the lowest-risk default.
What about legitimate interest?
Legitimate interest (Art. 6(1)(f)) can sometimes support marketing, but only after a documented balancing test, and it does not override national ePrivacy rules that require consent for electronic marketing in many cases. Where a “soft opt-in” exists for existing customers, it is limited to similar products, requires a clear opt-out at collection and in every message, and varies by country. Treat legitimate interest email marketing GDPR arguments as an exception you document, not a loophole for purchased or scraped lists. For deeper coverage, see our related guide on email opt-in and consent management best practices.
Building Compliant Email Lists: Pre-Subscription, During Capture & Validation
Compliance is cheapest when built into acquisition. Work through three stages.
Before subscription
- Publish a privacy notice that names your organisation, the purpose, the lawful basis, retention, recipients and how to exercise rights (Arts. 13-14).
- Write consent wording that states exactly what people will receive and how often.
- Use separate checkboxes for separate purposes, such as newsletters versus partner offers.
During capture
- Leave boxes unticked and link the privacy notice at the point of collection.
- Log the timestamp, source URL or form ID, IP address where appropriate, the exact consent text shown, and the version of the privacy notice.
- Send a double opt-in confirmation and record when it is clicked.
Validation: how do I validate an existing list?
Email list validation for GDPR is a provenance exercise first, a technical one second:
- Export every record with its source, date and consent evidence.
- Sort into three groups: provable consent, a documented alternative basis, and no evidence.
- Quarantine the “no evidence” group and stop sending to it.
- Run a re-permission campaign to uncertain records, with a clear opt-in action rather than “do nothing to stay subscribed”.
- Remove non-responders after a defined window, then run technical hygiene (bounces, role accounts, duplicates).
In our experience, the quarantine group is often larger than teams expect, particularly lists inherited from events, acquisitions or older CRM imports. Purchased lists should be treated as non-compliant unless you can verify the original consent covers your use.
List Maintenance & Hygiene: Remove, Update & Segment for Ongoing Compliance
Consent is not permanent, and a list that was clean last year may not be now. Build these routines:
- Honour unsubscribes immediately. The right to object to direct marketing (Art. 21(2)-(3)) is absolute. Suppress the address in every connected system, not just one platform.
- Maintain a suppression list. Keep the minimum data (the address or a hash) needed to ensure you never re-add someone who opted out.
- Apply a retention rule. GDPR sets no fixed period, so define your own, for example removing subscribers who have not opened or clicked in 18-24 months after a final re-engagement attempt. A clear GDPR data retention policy for email is easier to defend than ad hoc deletion.
- Segment by consent scope. Someone who agreed to product updates has not agreed to third-party promotions.
- Handle data subject rights. Access, rectification and erasure requests must be answered within one month. Know where list data lives, including exports, spreadsheets and ad platform audiences.
Vendor & Platform Audits: Assessing Third-Party Email Service Providers & Tools
How do I audit my email service provider?
Your ESP is usually a processor, and you stay accountable for it. A GDPR compliant email service provider is one that can show the following:
- A signed GDPR data processing agreement (DPA) meeting Article 28, covering instructions, confidentiality, security, sub-processors, assistance with rights requests, breach notification and deletion or return of data.
- A current sub-processor list with a notification process for changes.
- Lawful international transfer mechanisms, such as the EU-US Data Privacy Framework certification or Standard Contractual Clauses, where data leaves the EEA.
- Security evidence, such as ISO 27001 or SOC 2 reports, encryption in transit and at rest, and access controls.
- Product features that support compliance: consent fields, double opt-in, suppression management, export and deletion tools, and audit logs.
Do not rely on a “GDPR ready” badge. Ask for documents and test the features. Apply the same scrutiny to CRMs, form tools, enrichment services and ad platforms that touch the list. We cover this in more depth in our vendor audit checklist for marketing data providers. Your own security posture matters too; for reference, see how we approach our data security policy and our GDPR commitments.
Record-Keeping & Audit Trails: What to Document & How Long to Keep It
What records must I keep, and for how long?
A defensible GDPR audit trail for email includes:
- Consent records: who, when, how, what wording, which privacy notice version, and any withdrawal.
- Records of processing (Art. 30): required for most organisations that process data regularly, and listing purposes, categories, recipients, transfers and retention.
- Legitimate interest assessments where you rely on that basis.
- DPAs and vendor due diligence files.
- Rights request log: request date, action taken, response date.
- Breach register and DPIAs where applicable.
- Training and policy records.
GDPR does not state a retention period for these. The usual approach is to keep consent evidence for as long as you send marketing on that basis, plus a period tied to the legal limitation window in your jurisdiction, and to document that reasoning. Keep proof of an unsubscribe indefinitely in minimal form, since it protects the individual. This GDPR compliance documentation should be versioned, dated and findable within hours, not weeks.
GDPR Email Marketing Compliance Audit Checklist & Templates
Run this checklist quarterly. Each item maps to one of the Five Proofs.
- Consent: Every record has a source, timestamp and consent text. No pre-ticked boxes. Consent is unbundled.
- Consent: Withdrawal is one click and takes effect immediately across systems.
- Purpose: Privacy notice is current and linked at every form.
- Purpose: Any legitimate interest use has a written balancing test.
- Processor control: DPA signed with each vendor; sub-processors and transfer mechanisms reviewed in the last 12 months.
- Hygiene: Retention rule applied; inactive subscribers actioned; suppression list intact.
- Rights: Access and erasure requests can be fulfilled within one month; a log exists.
- Records: Article 30 record updated; evidence is stored centrally.
Useful templates to keep on file: a consent log schema, a re-permission email, a vendor due-diligence questionnaire, a legitimate interest assessment form, and a rights-request tracker.
Common Compliance Gaps & How to Fix Them Before an Audit
How does B2B differ from B2C?
GDPR protects individuals, so business contacts are covered whenever the address identifies a person. The difference lies mainly in ePrivacy rules, which vary by country. Some member states allow B2B marketing to corporate subscribers on an opt-out basis, while others, such as Germany, expect consent. Legitimate interest is easier to justify for relevant B2B outreach, but the right to object still applies. Check the rules of each country you target rather than assuming one standard.
What happens if I fail an audit, and how do I remediate quickly?
An internal or client audit failure is a prompt to act. A regulator finding can bring orders to stop processing, reprimands or fines of up to €20 million or 4% of global annual turnover for breaches of consent and core principles. The fastest remediation sequence is:
- Pause sending to records without proof of consent.
- Quarantine, then re-permission or delete them.
- Fix capture forms and consent logging.
- Sign missing DPAs and update your processing record.
- Document every step taken, since a visible remediation record carries weight with regulators.
Other gaps we see repeatedly: consent bundled into terms, unsubscribes processed only in the ESP, no retention rule, forgotten spreadsheet copies of the list, and vendors added without review. Each is cheap to fix before it is questioned.
Related reading: 7 Essential Email Templates Every Business Needs · Why Email Newsletters Still Matter in 2025
Frequently asked questions
Is double opt-in required under GDPR?
No, but it is the best way to prove consent and verify ownership of the address. Some national authorities expect it.
Can I email my existing customers without new consent?
Possibly, under a soft opt-in or legitimate interest, depending on your country’s ePrivacy rules. It is limited to similar products, requires a clear opt-out and should be documented.
How long can I keep an email address on my list?
GDPR sets no fixed period. Keep it only while it is needed for the stated purpose, and set a documented rule for removing inactive contacts.
Do I need a DPA with my email service provider?
Yes. If the provider processes personal data on your behalf, Article 28 requires a written data processing agreement.
Does GDPR apply to B2B email lists?
Yes, when the address relates to an identifiable person. Rules on consent versus opt-out for corporate contacts vary by country.
Can I keep a record of people who unsubscribed?
Yes. Keep a minimal suppression record so they are not re-added accidentally.
Next Steps
Most list problems are fixable once you can see them. Download our free GDPR Email Compliance Audit Checklist template to run the review above, then schedule a consultation with The Flick Studio’s compliance team. We will review your current list-management practices, vendor setup and documentation, and tell you plainly where the gaps are and what to fix first.